Threat intelligence from Check Point Research’s ThreatCloud AI shows a clear upward trend in cyberattacks during the second half of 2025 and the first half of 2026.
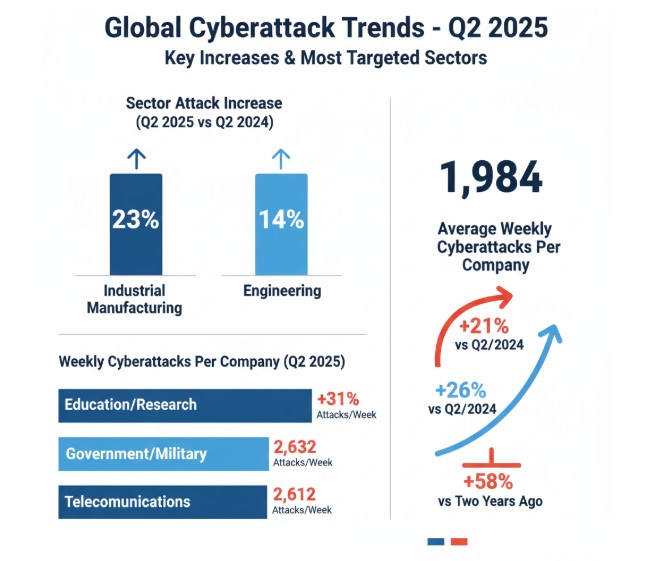
Organizations recorded an average of 1,984 weekly attacks per company recently — a 21% increase year-on-year and 58% higher than two years ago — signaling rising attack volumes and growing adversary sophistication.
Who was hit hardest?
Sectoral and regional breakdowns from H2 2025 and H1 2026 highlight where attackers concentrated their efforts.
| Category | Weekly Avg. per Organization | Year-over-Year Change |
| Global Average | 1,984 | +21% |
| Education & Research | 4,388 | +31% |
| Government / Military | 2,632 | +26% |
| Telecommunications | 2,612 | +38% |
| Industrial Manufacturing | — | +23% |
| Engineering | — | +14% |
Ransomware: public disclosures and regional concentration
Publicly available “shame site” disclosures of double-extortion incidents documented roughly 1,600 ransomware incidents globally in the same period.
North America accounted for the majority of these disclosures (about 53%), while Europe represented roughly 25% of recorded cases — showing that ransomware remains a transregional problem with visibility skewed toward markets where disclosures are more actively reported.
Why education and telecoms are attractive targets
The disproportionate targeting of the education/research sector is explained by a combination of limited cybersecurity investment and a wealth of exploitable credentials — students, staff and third-party logins present a large attack surface.
Telecom operators, by contrast, are targeted for their central role in critical communications infrastructure and the value of customer datasets they hold.
“As attacks grow in volume and sophistication — particularly in Europe and among critical sectors — security leaders must shift from reactive to preventive cybersecurity with continuous visibility and anticipatory controls.” as pointed out by several CISO’s.
Actionable measures for organizations
Drawing on the practical recommendations commonly issued by leading threat intelligence groups, the following controls should be prioritized.
- Invest in threat prevention: Deploy intrusion prevention systems (IPS), behavior-based anti-ransomware controls and real-time threat intelligence to block campaigns early.
- Harden networks and endpoints: Ensure next-generation firewalls, secure e-mail gateways and modern endpoint protection platforms are configured and patched.
- User awareness and phishing resilience: Run regular training and simulated phishing to reduce credential compromise and detection timelines.
- Backup & recovery readiness: Maintain immutable, segmented backups and exercise recovery procedures frequently to minimize downtime after ransomware or destructive attacks.
- Adopt Zero Trust principles: Enforce continuous identity verification, least privilege and micro-segmentation to limit lateral movement.
- Maintain active threat intelligence: Subscribe to sector feeds and monitor disclosure sites and vendor advisories to anticipate emerging TTPs (tactics, techniques and procedures).
Implications for security strategy
The shown figures underline three strategic realities for defenders: attackers are increasing both volume and sophistication; some sectors remain undersecured despite being attractive to adversaries; and regional differences in incident disclosure can distort perceived risk.
A defensible posture will require layered controls, robust identity governance, and an emphasis on preventing initial compromise rather than solely responding to incidents after the fact.
How RELIANOID supports organizations
At RELIANOID, we help organizations strengthen their resilience against the growing wave of cyberattacks by providing high-performance application delivery, secure proxy solutions, and advanced traffic visibility. Our technology enables IT and security teams to implement Zero Trust principles, ensure encrypted and reliable communications, and maintain business continuity even under attack. By combining efficiency with robust security features, RELIANOID empowers enterprises across industries to anticipate threats, reduce their attack surface, and protect critical digital assets.



Related Blogs